
Cyber Risk is Business Risk
Dear MDBC members,
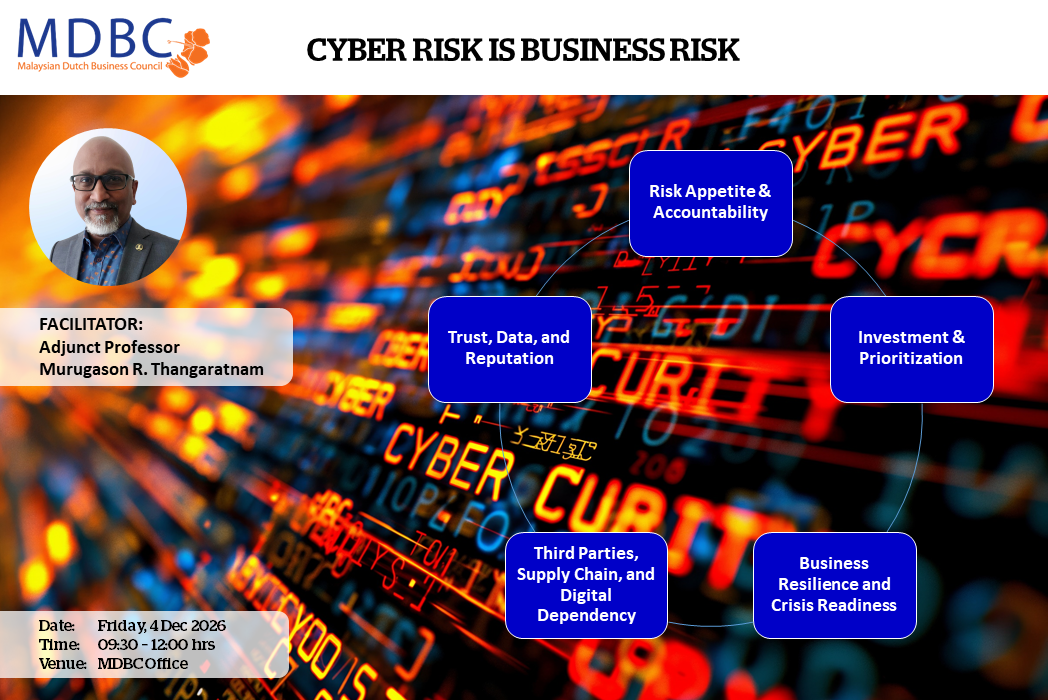
It’s 6:40 am and the phone rings. A major cyber – incident has hit your business overnight. Would you know who decides what, and how fast? Starting from that scenario, we work through the five decisions only leaders can make:
- Risk appetite and accountability: Who owns cyber risk and what are we prepared to accept?
- Investment and prioritization: Are we spending on what matters?
- Business resilience and crisis readiness: Could we keep operating after a major incident?
- Third parties, supply chain, and digital dependency: How much of our risk sits with others?
- Trust, data, and reputation: Could we show that we acted responsibly?
MDBC invites you to an executive roundtable on why cyber risk belongs in the boardroom, not just the IT department. We look at how AI is changing the threat landscape and our own exposure, as well as test three crisis scenarios together in a live table – top exercise. The session closes with a personal leadership commitment: one decision each participant will own.
Date: Friday, 4 December 2026
Time: 09:30 – 12:00 hrs
Venue: MDBC Office
Seats are limited to keep the discussion roundtable sized.
Cyber risk is business risk. Resilience, investment, supplier dependency, and trust are leadership decisions that can’t be handed off, and AI is raising the stakes on every one of them. You’ll leave knowing which decision to own first.
Format: Interactive and discussion – led, with table exercises and a table – top simulation. This is a working session, not a lecture.
Chatham House Rule: Ideas may be shared, but names and companies may not, so you can speak openly.
Who Should Attend:
- CEOs, Managing Directors, and Country Heads
- Board Members and Non – Executive Directors
- CFOs, COOs, and Heads of Risk, Compliance, and Legal
- CIOs, CISOs, and Senior Technology Leaders
- Senior leaders responsible for operations, supply chain, data, or brand reputation
***
Itinerary: This roundtable is held under the Chatham House Rule: ideas may be shared, but names and companies should not be.
09:30 – 10:00 hrs: Registration
10:00 – 10:08 hrs: Welcome Remarks and Opening. Setting the stakes and ground rules
10:08 – 10:15 hrs: The 06:40 am call… A scenario and quick pulse check
10:15 – 10:25 hrs: Decision 1: Risk appetite and accountability. Who owns cyber risk and what are we prepared to accept?
10:25 – 10:33 hrs: Decision 2: Investment and prioritization. Are we spending on what matters?
10:33 – 10:41 hrs: Decision 3: Business Resilience and Crisis Readiness. Could we keep operating after a major incident?
10:41 – 10:46 hrs: Stand and swap pause. Change tables, meet new perspectives.
10:46 – 10:54 hrs: Decision 4: Third parties, supply chain, and digital dependency. How much of our risk sits with others?
10:54 – 11:02 hrs: Decision 5: Trust, data, and reputation. Could we show that we acted responsibly?
11:02 – 11:27 hrs: AI Raises the Cyber Stakes. How AI changes the threat and our own exposure.
11:27 – 11:47 hrs: Crisis table – top. Three scenarios tested together.
11:47 – 11:56 hrs: Leadership commitment. One decision each of us will own.
11:56 – 12:00 hrs: Closing. Key messages to take back.
REGISTRATION:
Please register online via the link below.
By clicking and registering online you acknowledge the event guidelines.
Seats are limited to keep the discussion roundtable sized.
Please register no later than Wednesday, 2 December (12:00 hrs).